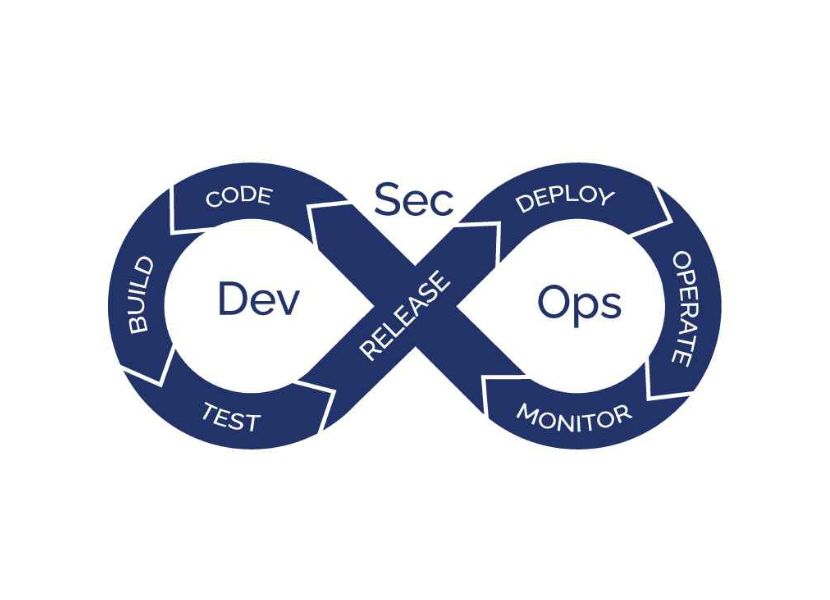
Module 1: Introduction to DevSecOps
Task: Introduction to DevSecOps:
- Definition of DevSecOps
- How it differs from DevOps
- Real-world examples of security failures
- DevSecOps principles and benefits
Outcomes:
- Clear understanding of what DevSecOps is and why it’s important
Module 2: SDLC, Threats & Attack Vectors
Task: Threat Modeling Basics:
- Overview of SDLC stages
- Introduction to security touchpoints in SDLC
- Understanding common attack vectors
- Basic intro to STRIDE model
Outcomes:
- Ability to identify threats across SDLC stages
Module 3: OWASP Top 10 – Part 1
Task: OWASP Top 10 (Part 1):
- Cover top 5: Injection, Broken Authentication, Sensitive Data Exposure, XML External Entities (XXE), Broken Access Control — with examples
Outcomes:
- Familiarity with most critical web application risks
Module 4: Secure Code Practices
Task: Secure Coding Guidelines:
- Understanding secure coding principles: input validation, encoding, error handling, password management, basic intro to SAST
Outcomes:
- Knowledge of how to write more secure code
Module 5: Static Code Scanning (SonarQube)
Topic: Run SonarQube Scan:
- Install SonarQube using Docker
- Scan a JavaScript or Java project
- Review bugs
- Vulnerabilities
- Code smells
Outcomes:
- Able to analyze code using SonarQube
Tools:
- SonarQube
- Docker
Module 6: Introduction to CodeQL
Topic: Run CodeQL:
- Install CodeQL CLI
- Use GitHub CodeQL repo
- Run analysis
- View and understand query results
- Explore query customization
Outcomes:
- Understand how to use CodeQL for deep code analysis
Tools:
- CodeQL
Module 7: CI/CD Pipeline Overview
Topic: CI/CD Basics:
- Understand CI/CD stages
- Tools overview (GitHub Actions, GitLab)
- Explain where security tools can be integrated
- Pipeline visualization
Outcomes:
- Know CI/CD stages and security injection points
Tools:
- GitHub Actions
Module 8: Secure CI with SonarQube/Snyk
Topic: CI with Security Scans:
- Integrate SonarQube or Snyk in a pipeline
- Trigger automatic scans on pull request
- See scan reports and logs
Outcomes:
- Hands-on security in CI pipelines
Tools:
- SonarQube
- Snyk
Best Online DevSecOps Training in Pakistan
Most pipelines in this region were built for speed and had security added afterwards, usually after an incident. DevSecOps reverses that order. You learn to put scanning, secrets management and policy enforcement inside the pipeline itself, so insecure code stops before it ships rather than after it is exploited.
This is a 30 hour live program across 8 modules, delivered live online across Pakistan. It assumes you already understand what a pipeline is. If you do not, take the DevOps Master Program first, then come back to this one.
The demand driver here is straightforward. Banks, fintechs and any company handling regulated data in Pakistan now audit their software supply chain. The engineers who can demonstrate secure pipeline experience are a small group, and the salary reflects it.
Key Benefits of DevOps
You become the person who unblocks compliance
Security reviews are where releases go to die. An engineer who can build controls into the pipeline turns a multi week review into an automated gate. That visibility inside an organisation is worth more than most technical skills.
Scarce skill, thin local competition
Plenty of engineers in Pakistan can build a pipeline. Very few can build one that passes a security audit. That gap is what pushes DevSecOps compensation above general DevOps roles.
You learn the tooling that regulated employers require
Static and dynamic analysis, dependency and container scanning, secrets management, and policy as code. These are the specific controls that appear in audit checklists, not abstract security theory.
It pairs naturally with formal security certification
Many students combine this with CompTIA Security+ SY0-701 for the fundamentals, or move toward Certified Information Systems Security Professional if they are heading into a security leadership track.
Cloud security becomes a logical next step
Students working primarily on Microsoft stacks often continue into Azure Security Engineer AZ-500, which applies the same thinking to cloud identity and platform controls.
Why Choose ItechNets for DevSecOps
Proof rather than promises
15,000+ professionals trained, a 96% pass rate, 8,500+ alumni and 150+ hiring companies in our network. We publish these because most training providers in this market publish nothing measurable at all.
You break things in a lab, not in production
The labs include deliberately vulnerable applications. You run the scan, see the finding, fix it and watch the gate pass. Reading about a vulnerability class and catching one in your own pipeline are different kinds of knowledge.
We are an authorised exam centre in our own right
We operate an authorised Pearson VUE test centre in DHA Phase IV, Lahore, covering Microsoft, AWS, Google Cloud, Cisco, CompTIA and VMware exams.
Trainers from working security teams
Our instructors have handled real incidents and real audits. That experience is the difference between teaching a tool and teaching judgement about when a finding actually matters.
Frequently Asked Questions About DevSecOps
What is the difference between DevOps and DevSecOps?
DevOps automates the path from code to production. DevSecOps adds automated security controls to that path so vulnerabilities, exposed secrets and unsafe dependencies are caught by the pipeline instead of by a person reviewing after the fact.
Do I need a security background to take this course?
No, but you do need pipeline familiarity. Security concepts are taught from the ground up. Pipeline concepts are not.
Is DevSecOps in demand in Pakistan specifically?
Yes, and it is concentrated. Demand is strongest in banking, fintech, telecom and any firm delivering software to clients in Europe, where the client’s own compliance requirements flow down to the vendor.
How long is the program and when do batches start?
30 hours across 8 modules, typically over 8 weeks of evening sessions on PKT. Batch dates are published on the course catalogue and our team can confirm the next available seat.
Will I get a certificate at the end?
You receive an iTechNets completion certificate. DevSecOps has no single dominant vendor exam, which is why most students pair it with a recognised security certification for the credential line on their CV.