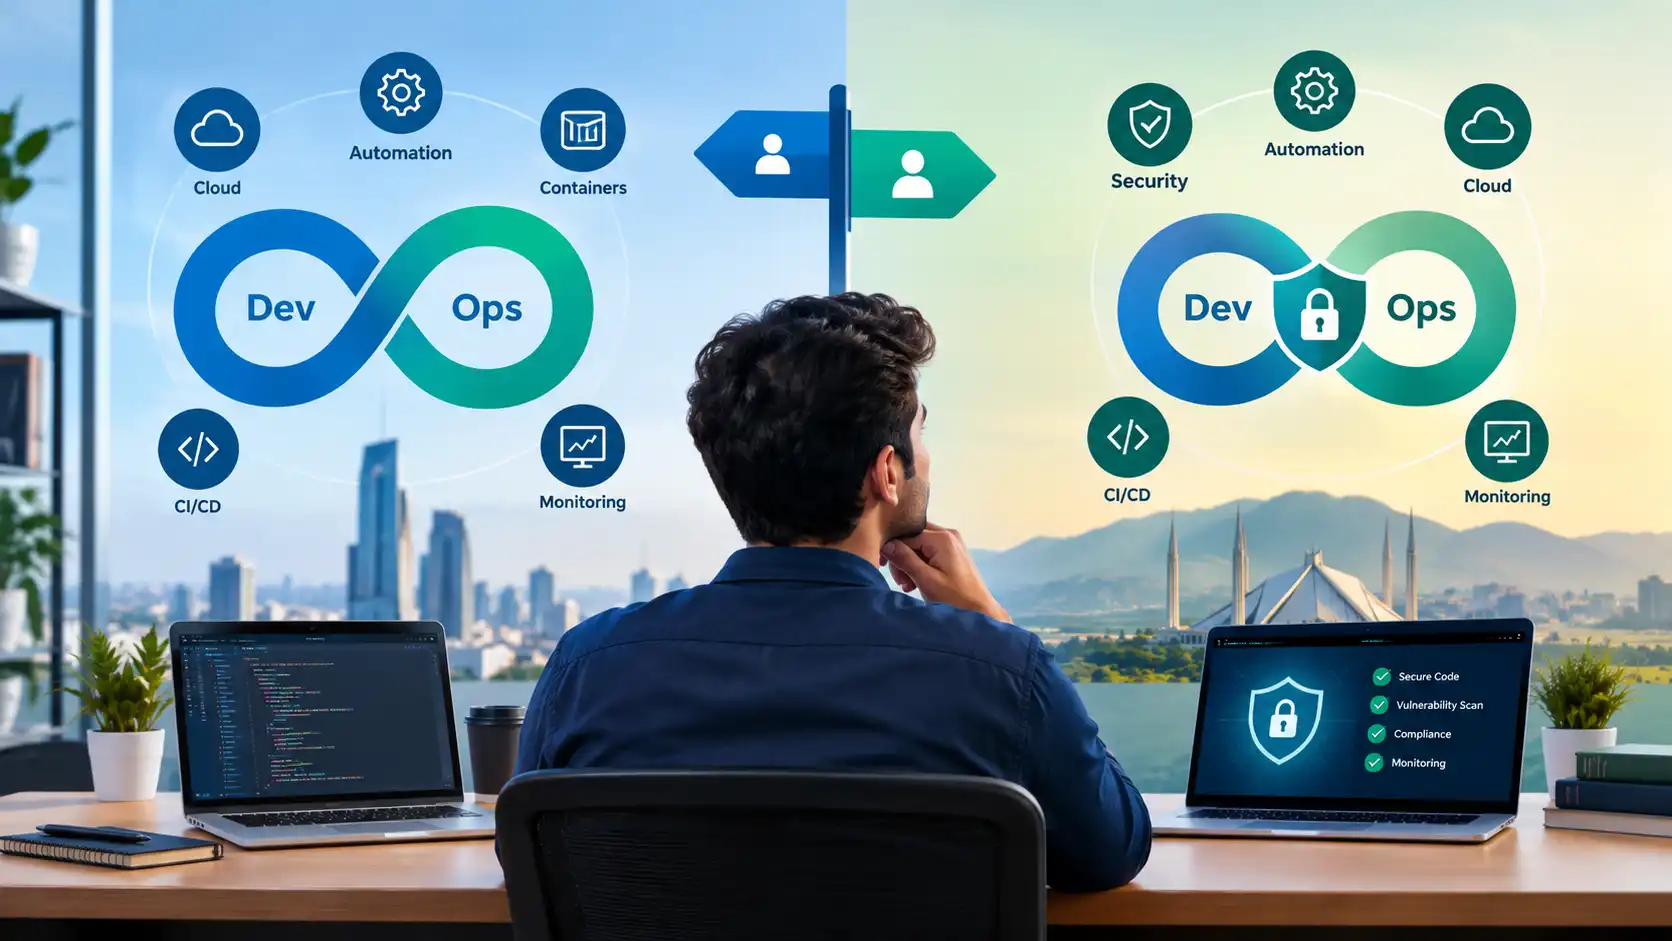
DevOps and DevSecOps share 70 percent of their tooling. They differ in who you answer to, what breaks your week, and which budget line pays your salary. In Pakistan the choice now carries a regulatory dimension that did not exist eighteen months ago. This comparison gives you the decision criteria, not a definition list.
Why This Question Now Has a Regulatory Answer
Pakistan National Cyber Emergency Response Team directed all public and private organisations in July 2026 to deploy Security Operations Centres within six months. The same briefing cited 927 cyberattacks across 2024 and 2025 and 253 attacks in 2026 alone, including a ransomware incident at a government entity. Pakistan Information Security Framework 2026 has been presented to parliament, and sectoral response teams are being deployed at the State Bank, SECP, NEPRA, OGRA, HEC and CAA.
Read that as a hiring forecast. Every bank, insurer, power utility, telecom operator and listed company now needs people who can wire security controls into build pipelines and produce audit evidence on demand. That is DevSecOps work, and the demand is compliance-driven rather than discretionary. Compliance-driven demand survives budget cuts.
The Two Roles Defined by Deliverable
What a DevOps Engineer Delivers
A DevOps engineer delivers deployment velocity and system reliability. The scorecard is deployment frequency, lead time for changes, change failure rate and mean time to recovery. You own pipelines, infrastructure as code, container orchestration, observability and cloud cost. You report into engineering.
What a DevSecOps Engineer Delivers
A DevSecOps engineer delivers the same pipeline plus provable control. The scorecard adds mean time to remediate a vulnerability, percentage of builds scanned, secrets exposure incidents, and audit findings closed. You own static and dynamic application security testing, software composition analysis, container image scanning, secrets management, policy as code and compliance evidence. You report into engineering but you answer to risk and audit.
The practical difference: a DevOps engineer is asked why the deploy took nine minutes. A DevSecOps engineer is asked to prove that no unscanned artefact reached production in the last quarter.
Side-by-Side Comparison
| Dimension | DevOps | DevSecOps |
| Primary objective | Ship faster with fewer failures | Ship faster without introducing unmanaged risk |
| Core tooling | Git, Jenkins or GitHub Actions, Docker, Kubernetes, Terraform, Ansible, Prometheus, Grafana | All of the left column plus SAST, DAST, SCA, image scanning, secrets vaults, policy engines, SIEM integration |
| Key metrics | Deployment frequency, lead time, change failure rate, MTTR | MTTR for vulnerabilities, scan coverage, critical findings age, audit pass rate |
| Stakeholders | Engineering managers, product owners | Engineering, CISO, internal audit, external regulator |
| Typical Pakistani employer | Export software houses, product startups, agencies | Banks, fintechs, telecom operators, government contractors, listed companies |
| Entry difficulty | Moderate, learnable from a support or sysadmin base | Higher, expects DevOps competence plus security fundamentals |
| Job volume in Pakistan | Larger pool of openings today | Smaller pool, faster growth, less competition per opening |
| Pay position | Strong | Typically a premium over the equivalent DevOps band because the supply of qualified candidates is thinner |
Pakistani cybersecurity pay data reported in 2026 places entry SOC and junior analyst roles at roughly PKR 40,000 to 90,000 per month, mid-level offensive and engineering roles at PKR 90,000 to 180,000, and senior security engineering or SOC leadership at PKR 180,000 to 350,000 and above. Compare that with reported DevOps averages near PKR 100,000 per month and the senior premium becomes visible.
Which Path Fits Your Background
Match your starting point to the shorter route. Switching later is possible, but the first eighteen months compound.
| Your current background | Recommended path | Reasoning |
| Software developer | DevOps first | You already read code and understand build systems. Pipeline ownership is a short step. |
| Network or system administrator | DevOps first | Linux and networking transfer directly. Add scripting and containers. |
| SOC analyst or security graduate | DevSecOps directly | You have threat context already. Add pipelines and infrastructure as code. |
| Fresh graduate, no experience | DevOps first, DevSecOps at month 18 | Security tooling assumes you can already build and deploy the thing you are securing. |
| QA or test automation engineer | Either, DevSecOps has the edge | Test automation habits map cleanly onto security gates in a pipeline. |
| Banking or fintech IT staff | DevSecOps directly | Your employer is now under a SOC and compliance mandate. Internal moves are faster than external hires. |
Pakistan Employer Demand Map
| Sector | Hires more of | Driver |
| Export software houses | DevOps | Client service level agreements and release cadence |
| Banks and microfinance | DevSecOps | SOC deployment mandate and State Bank sectoral oversight |
| Fintech and payment processors | DevSecOps | Card scheme requirements plus regulator scrutiny |
| Telecom operators | Both | Hybrid infrastructure at scale plus critical national infrastructure status |
| Government and public sector projects | DevSecOps | Pakistan Information Security Framework compliance and CERT reporting |
| Product startups | DevOps | Small teams optimise for speed before audit readiness |
Certification Sequencing for Each Path
| Stage | DevOps track | DevSecOps track |
| Foundation | Linux administration and one scripting language | Linux administration plus security fundamentals |
| Core | Container orchestration and infrastructure as code | Container orchestration plus vulnerability management and analytics |
| Cloud specialisation | Cloud administrator or architect associate | Cloud security specialisation |
| Expert | Cloud DevOps engineer professional level | Cloud security engineer plus governance credentials |
For the DevOps track, the DevOps Master Program covers foundation through orchestration, and the Microsoft Azure DevOps AZ-400 course is the expert-level credential enterprises recognise. For the DevSecOps track, start with CompTIA Security+ training, progress through CompTIA CySA+ for threat detection, then specialise with the DevSecOps programme. Candidates targeting bank SOC roles should add Microsoft SC-200 security operations analyst training, and those on AWS estates should target the AWS Certified Security Specialty.
Both tracks need container competence. The Certified Kubernetes Administrator programme is the shared prerequisite, because you cannot secure an orchestration platform you cannot operate.
Time and Cost to First Offer
| Factor | DevOps | DevSecOps |
| Realistic study time from a general IT base | 9 to 12 months | 14 to 18 months |
| Minimum certifications employers expect | One cloud associate credential | One security credential plus one cloud credential |
| Portfolio expectation | Working pipeline with rollback and monitoring | Pipeline with scanning gates plus a written control evidence pack |
| Openings available today in Pakistan | Higher volume | Lower volume, higher growth rate |
| Competition per opening | Heavy | Lighter, because few candidates hold both skill sets |
The DevSecOps route costs roughly five additional months and one extra certification. It buys access to a smaller applicant pool inside regulated employers who cannot defer hiring. That is the trade.
Career Ceiling and Switching Cost
DevOps leads to site reliability engineering, platform engineering and cloud architecture. DevSecOps leads to application security engineering, cloud security architecture and eventually security leadership roles that report to a CISO. Moving from DevOps to DevSecOps later costs about six months of security study. Moving the other way is faster, because operational fundamentals are already in place.
Neither path is a dead end. The mistake is attempting both simultaneously as a beginner, which produces shallow competence in each and a CV that fails both screens. Background reading on why DevOps skills are becoming essential across IT roles explains why the operational base matters either way.
Frequently Asked Questions
Does DevSecOps pay more than DevOps in Pakistan?
At senior level, usually yes, because regulated employers compete for a thin candidate pool. At entry level the gap is small, and DevOps roles are easier to obtain because there are more of them.
Can I move into DevSecOps without a security certification?
You can, but the screening is harder. Regulated employers use certifications as an audit-defensible hiring filter. A recognised security credential shortens the shortlist decision. An entry-level route such as Certified in Cybersecurity covers the vocabulary gap quickly.
Is DevSecOps a real job title or a DevOps job with extra duties?
In Pakistani startups it is frequently the same person with added duties. In banks, telecom operators and government contractors it is a distinct headcount with a separate reporting line, and the SOC mandate is accelerating that separation.
Which path is safer over the next five years?
DevSecOps demand is tied to regulation, which does not reverse. DevOps demand is tied to software delivery volume, which is also growing. Both are durable. DevSecOps is currently the less crowded of the two.
Choose Your Track and Start With a Structured Plan
Pick the path that matches your background, not the one with the better acronym. Browse the DevOps and cloud training track or the full course catalogue to see how the two sequences differ, then talk to a training advisor who can review your current experience and recommend the shorter route to your first offer.